Key Takeaways
- An ISO 45001 audit checks whether an occupational health and safety management system meets the requirements of ISO 45001:2018, as amended in 2024.
- There are three kinds: internal audits run by your own team, supplier audits of contractors, and certification audits by an accredited body.
- Internal audits are not optional. Clause 9.2 requires them at planned intervals, under a defined audit programme.
- Certification happens in two stages: a readiness and document review, followed by an audit of how the system works in practice.
- Once certified, expect a surveillance audit at least once a year and a full recertification audit every three years.
- A revised edition of ISO 45001 is expected in the first half of 2027. Until it is published, the 2018 edition with Amendment 1:2024 applies.
An ISO 45001 audit is a structured check of whether an occupational health and safety management system (OHSMS) meets the requirements of ISO 45001:2018, the international standard for OH&S management.
Though ISO 45001 is applicable to any organization looking to implement an OHSMS, regardless of size, industry, or geographic location, it’s particularly valuable for high-risk industries like construction, manufacturing, mining, oil and gas, etc. To get certified, an organization runs its own internal audits under clause 9.2, then passes a two-stage certification audit by an accredited certification body.
What Is an ISO 45001 Audit?
The current version is ISO 45001:2018 with Amendment 1:2024, which added climate change to clauses 4.1 and 4.2. It replaced OHSAS 18001, and a revised edition is expected in 2027.
Organizations certified to OHSAS 18001 had three years to migrate, and the IAF extended the deadline by six months because of COVID-19, to 30 September 2021. ISO 45001 uses the Plan-Do-Check-Act (PDCA) methodology, adopting a systematic approach to managing occupational health and safety risks, and can be integrated with other ISO standards.
ISO 45001 audits are formal, systematic examinations of an organization’s occupational health and safety management system to verify compliance with the ISO 45001 standard. These audits evaluate whether the organization’s health and safety practices are effectively implemented, maintained, and continually improved.
Types of ISO 45001 Audits
ISO 45001 audits are primarily categorized into internal and external audits, each serving distinct purposes in the certification process.
| Audit type | Who runs it | Purpose | When |
|---|---|---|---|
| Internal (first-party) | Your own trained auditors, independent of the area audited | Check conformity and effectiveness; find gaps before external audits | At planned intervals set in your audit program |
| Supplier (second-party) | Your auditors or a firm acting for you | Check a contractor’s or supplier’s safety controls | Before onboarding and on a risk basis |
| Certification (third-party) | Accredited certification body | Decide whether to grant certification (stage 1 and stage 2) | Once, at initial certification |
| Surveillance and recertification | Accredited certification body | Confirm the system still conforms; renew the certificate | Surveillance at least yearly; recertification before the 3-year expiry |
ISO 45001 Internal Audits
Internal audits are conducted by the organization’s trained staff to verify compliance and identify improvements before external assessments. Often called “first-party audits,” they’re performed by individuals independent of the audited processes to maintain objectivity. The primary goals of ISO 45001 internal audits include:
- Confirming compliance with ISO requirements and organizational policies
- Assessing the effectiveness of safety controls
- Finding opportunities to enhance safety performance
- Preparing for external certification audits
ISO 45001 Supplier Audits
Also known as “second-party audits,” these occur when one organization evaluates a contractor’s or supplier’s safety management system against ISO 45001 requirements. They help companies verify that their supply chain partners maintain appropriate safety standards, reducing operational risks and ensuring consistent safety performance across the value chain.
The process typically examines safety documentation, workplace conditions, and training programs to confirm adequate control of occupational health and safety risks. These audits can be conducted either by the organization’s own qualified staff or by hired external auditors acting on behalf of the organization.
ISO 45001 External & Certification Audits
External audits, also known as ‘third-party audits’, are performed by independent third-party auditors or certification bodies, who evaluate your organization’s compliance with ISO 45001 requirements. These audits provide an objective assessment of your OHSMS, identifying non-conformities and areas needing improvement. They are crucial for validating the effectiveness of your health and safety practices and demonstrating compliance to stakeholders.
Certification audits are conducted by accredited certification bodies to determine if your organization meets ISO 45001 requirements and ultimately delivers the official ISO 45001 certification.
The certification audit has two stages:
- Stage 1: A preliminary assessment of your organization’s readiness for the certification audit, including a review of documentation and planning.
- Stage 2: A thorough evaluation of the implementation and effectiveness of your OHSMS, leading to the decision on certification.
Surveillance and Recertification Audits
An ISO 45001 certificate is valid for three years. During that cycle, the certification body carries out surveillance audits, at least once a year, that sample parts of the OHSMS rather than repeating the full stage 2 audit. Before the certificate expires, a recertification audit reviews the whole system again. Open nonconformities from the last visit are usually the first thing the auditor checks, so keep corrective action records current between audits.
What Do ISO 45001 Auditors Check?
During ISO 45001 audits, several critical aspects are assessed to ensure compliance and effectiveness of the OHSMS.
Context of the Organization (Clause 4)
Auditors check that you have identified the internal and external issues that affect the OHSMS and, since Amendment 1:2024, decided whether climate change is a relevant issue. This includes recognizing worker needs, legal requirements, and operational conditions. It helps you tailor the OHSMS to address specific challenges and opportunities within your organization.
Leadership and Worker Participation (Clause 5)
Auditors evaluate how top management demonstrates leadership and commitment to occupational health and safety. This includes the OH&S policy, objectives, and evidence that non-managerial workers are consulted and take part in decisions (clause 5.4).
Hazard Identification and Risk Assessment (Clause 6.1)
Auditors examine the processes in place for hazard identification, risk assessment, and determining appropriate control measures to prevent incidents.
👉 For businesses specifically dealing with chemicals and hazardous substances, a digital COSHH assessment ensures compliance with workplace safety regulations. A risk assessment app can help them perform job hazard assessments to identify potential risks and prevent severe incidents.
Legal and Other Requirements (Clauses 6.1.3 and 9.1.2)
Auditors verify that your organization has identified applicable laws and regulations and has implemented processes to comply with them. This includes maintaining up-to-date records and demonstrating compliance with statutory obligations.
Operational Control and Emergency Preparedness (Clause 8)
Implementing operational controls to manage identified risks and preparing for potential emergencies are key components of the OHSMS. Auditors assess the effectiveness of these controls and the readiness of the organization to respond to emergency situations.
Incidents, Nonconformities and Performance Monitoring (Clauses 9.1 and 10.2)
Auditors evaluate how incidents are reported, investigated, and analyzed to prevent recurrence. They review incident reports, corrective actions taken, and the use of performance indicators to track health and safety objectives.
👉 Explore how a mobile incident reporting app enables real-time reporting and investigation, ensuring quick corrective measures. Moreover, a strong near-miss incident reporting system helps identify potential hazards before they lead to major incidents.
Competence and Awareness (Clauses 7.2 and 7.3)
Auditors examine training programs, competency assessments, and awareness initiatives to ensure employees are competent and aware of their roles within the OHSMS.
Documented Information (Clause 7.5)
Maintaining accurate and up-to-date documentation is essential to demonstrate compliance with ISO 45001. Auditors review policies, procedures, and records to ensure they are properly managed and reflect current practices.
Management Review and Continual Improvement (Clauses 9.3 and 10.3)
During an ISO safety audit, auditors assess how top management reviews system performance, considers feedback, and implements changes to improve health and safety outcomes, identify opportunities for improvement, and enhance the effectiveness of the OHSMS.
How to Conduct an ISO 45001 Internal Audit
Clause 9.2 requires internal audits at planned intervals under an audit program, and most organizations follow the six steps below, using ISO 19011:2026 for audit method guidance.
Create an ISO 45001 Audit Plan
Set an audit program that covers every OHSMS process and site over the cycle, then write an ISO 45001 audit plan for each audit with its scope, criteria, schedule, auditors, and the people you will interview.
An ISO 45001 audit plan should state:
- Audit objective — what this audit is meant to establish
- Scope — the sites, processes, shifts, and clauses covered
- Criteria — ISO 45001:2018 clauses, legal requirements and your own procedures
- Dates and timetable — when each area is audited and for how long
- Auditors and auditees — who audits, and who they need from each area
- Opening and closing meetings — when they happen and who attends
- Resources and logistics — site access, PPE, escorts, and any systems the auditor needs to view
👉 Find out how using a mobile app for workplace inspections speeds up data collection and reporting for internal audits.
Establish a Team
Select qualified auditors who understand ISO 45001 requirements. Ensure they are independent of the processes they evaluate to maintain objectivity.
Use Digital Checklists
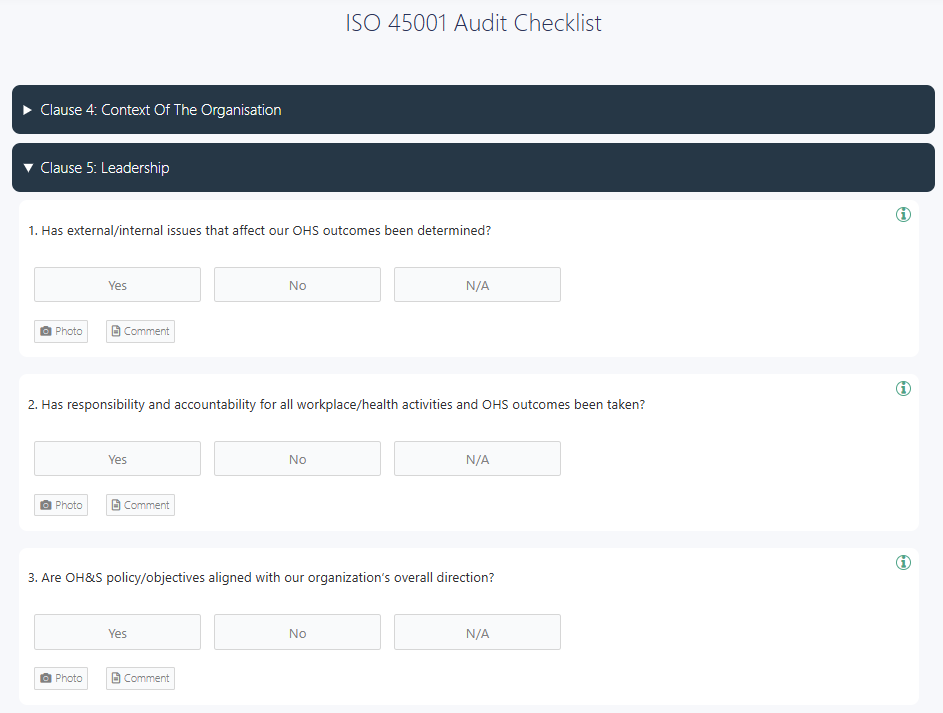
Use a structured, digital checklist covering key areas such as policy compliance, hazard identification, legal adherence, emergency preparedness, and training. This ensures no critical aspect is overlooked. Use the ISO 45001 audit checklist to structure each audit against the clauses.
👉 GoAudits offers a free ISO 45001 audit checklist to help you perform a complete health and safety audit of your organization and prepare for the ISO 45001 certification process.
Conduct the Internal Audit
Perform the audit through document reviews, interviews, observations, and process evaluations. Gather objective evidence to identify strengths and areas for improvement.
Write the ISO 45001 Audit Report
An ISO 45001 audit report records what was audited, what the auditor found, and what happens next. Write it while the evidence is fresh, and give each finding a clause reference, the evidence behind it, and a grade.
Use this structure:
- Report details: organization, site, audit reference, dates, lead auditor and audit team.
- Objectives, scope and criteria: sites, processes and shifts covered; ISO 45001:2018 with Amendment 1:2024 clauses audited; legal and other requirements; internal procedures.
- Method and sampling: documents and records reviewed, people interviewed (including non-managerial workers), areas and activities observed.
- Summary conclusion: whether the OHSMS conforms and is effective, and the audit team’s overall judgment.
- Findings table: finding number, clause, finding statement, objective evidence, grade.
- Good practice observed.
- Corrective actions: owner, due date, root cause, and how closure will be verified.
- Status of findings from the previous audit.
- Distribution list and sign-off.
Grade findings consistently:
| Grade | Meaning | Example |
|---|---|---|
| Major nonconformity | A requirement is not met in a way that puts the system’s ability to achieve its intended results in doubt | No internal audits have been carried out since certification |
| Minor nonconformity | A requirement is not met, but the system still works | One department’s training records are incomplete |
| Opportunity for improvement | No requirement is breached, but practice could be better | Near-miss reports are logged but trends are not reviewed |
For a ready format, see our non-conformance report template.
👉 Understanding workplace incident report examples can help standardize reporting formats and ensure consistency, while using safety observation reports can help identify recurring safety concerns, track trends, and support proactive risk mitigation efforts.
Implement Corrective Actions
Address identified nonconformities by conducting root cause analyses, developing corrective action plans, verifying implementation, and scheduling follow-up audits to ensure sustained compliance.
How to Get ISO 45001 Certified: The Certification Process
Here are the steps to implement ISO 45001 and achieve the certification.
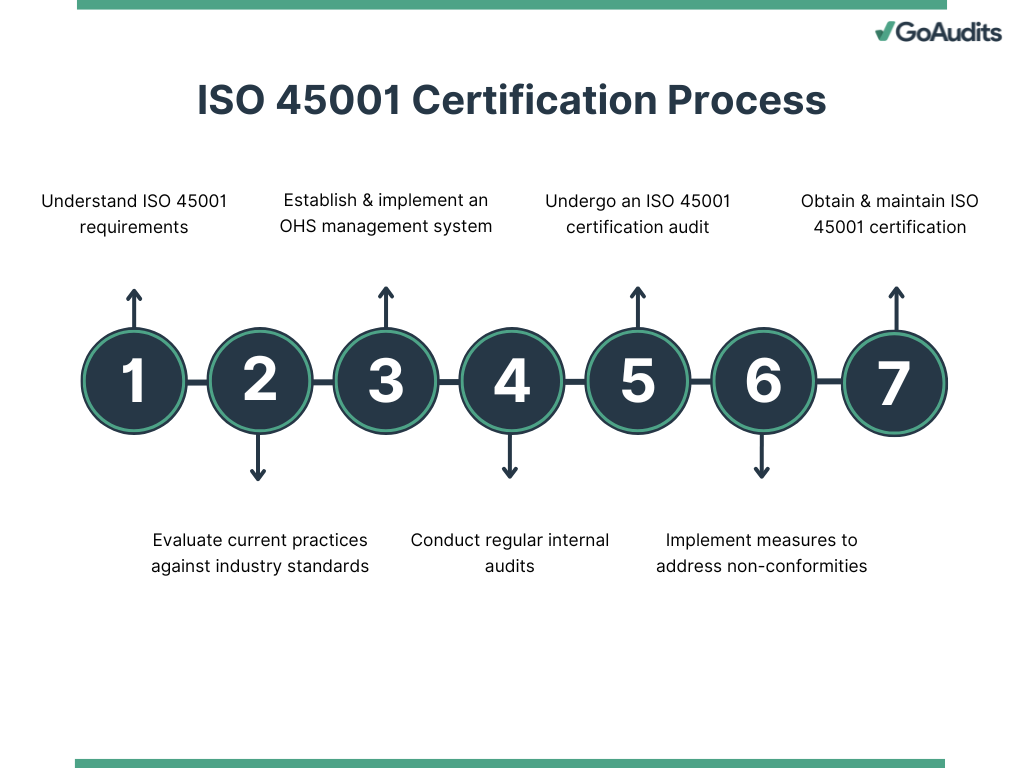
1. Understand ISO 45001 Requirements
Begin by familiarizing yourself with ISO 45001 requirements, which outline the criteria for an effective OHSMS. It will help you grasp the necessary components and the benefits of implementing such a system within your organization. Work through the ISO 45001 requirements checklist to map each clause to what you already have in place.
2. Conduct a Gap Analysis
Evaluate your current health and safety practices against ISO 45001 standards to identify discrepancies. This assessment will highlight areas requiring improvement and assist in prioritizing actions to align with the certification requirements.
3. Establish and Implement an OHSMS
Build an OHSMS that fits your organization’s hazards, size, and legal duties. Secure leadership commitment to allocate necessary resources, define clear health and safety policies, and set measurable objectives. Ensure that roles and responsibilities are well-defined, and engage employees at all levels.
4. Conduct Internal Audits
Perform regular internal audits to assess the effectiveness of your OHSMS. These audits will help identify non-conformities and areas for improvement, ensuring that your system remains compliant with ISO 45001 requirements.
5. Prepare for and Undergo a Certification Audit
Select an accredited certification body to conduct the external certification audit. This process typically involves a two-stage assessment: an initial evaluation of your organization’s readiness, followed by a detailed on-site audit to verify compliance with ISO 45001 requirements.
6. Address Non-Conformities
If the certification audit uncovers any non-conformities, develop and implement corrective actions promptly. Document these actions thoroughly to demonstrate your organization’s commitment to continuous improvement in occupational health and safety practices.
7. Obtain and Maintain Certification
Upon successful completion of the certification audit and resolution of any non-conformities, your organization will receive ISO 45001 certification. Certificates run on a three-year cycle: the certification body carries out a surveillance audit at least once a year and a recertification audit before the certificate expires.
What Changes With the Next ISO 45001 Edition
As of November 2026, the current standard is ISO 45001:2018 with Amendment 1:2024. The amendment asks organizations to decide whether climate change is a relevant issue (clause 4.1) and notes that interested parties can have climate-related requirements (clause 4.2).
A revised edition reached the Draft International Standard stage in 2026, with the ballot closing on 9 September. ISO expects publication in the first half of 2027, though the timetable may change, and the transition period will only be set after publication. Until the new edition is published, audits and certification continue against the 2018 edition.
Streamline ISO 45001 Internal Audits with GoAudits
Conducting internal audits for ISO 45001 compliance is essential for maintaining an effective OHSMS. GoAudits safety inspection software is an all-in-one platform for audits, inspections, and compliance. It replaces paper and spreadsheet audits with mobile checklists, instant reports, and tracked corrective actions.
- Choose from our library of pre-built templates, customize them to meet ISO 45001 requirements, or create your own using a simple drag-and-drop interface.
- Conduct internal audits on a mobile app, even offline, and sync results when you reconnect.
- Automatically generate detailed reports after each audit, pre-populated with photos, timestamps, and geolocation. Share them with managers and auditees as soon as the audit ends.
- Assign corrective actions during inspections directly within the app, track progress, and set reminders to ensure timely resolution of identified issues.
- Set up automatic report sharing, task assignments, and reminders.
- Use dashboards to track scores and recurring findings across sites.
UK haulage and warehousing firm Miniclipper Logistics moved its H&S audits from Excel forms to GoAudits after testing six providers. Audits went from every six months to monthly, and audit responsiveness rose from 65% to 97%.
After trialling GoAudits in tandem with our selected audit system, we found rather quickly that GoAudits provided a far better system in terms of ease-of-use, template design options, layout, flow, functionality, actions, reporting and excellent customer support.
Steve Blaydon, Business Process Manager, Miniclipper Logistics.
Related Safety Audit Templates
GoAudits offers a wide range of health and safety audit checklists and ISO audit templates. You can sign up for free and start using these checklists.
- Occupational Health and Safety Checklist
- Workplace Safety Audit Checklist
- Chemical Safety Checklist – COSHH
- JSA Form – Job Safety Analysis Checklist
- Safety Audit Template
- HSE Management System Template
- Near Miss Incident Report
- Hazard Identification Form
- Incident Investigation Template
Why are ISO 45001 Audits Important for Workplace Safety?
ISO 45001 audits are essential for enhancing workplace safety and offer several key benefits:
- Audits provide a structured approach to identifying and assessing occupational health and safety risks, enabling organizations to proactively mitigate hazards and prevent incidents.
- Implementing ISO 45001 through regular audits helps decrease work-related injuries and illnesses, leading to improved safety performance.
- By minimizing workplace accidents, organizations can reduce costs associated with compensation claims, legal liabilities, and operational downtime, resulting in overall financial benefits.
- A safe working environment fosters employee satisfaction and morale, contributing to increased productivity and operational efficiency.
- Regular audits ensure adherence to occupational health and safety regulations, helping organizations avoid legal penalties and maintain compliance with industry standards.
- Audits assess and strengthen emergency response plans, enhancing an organization’s ability to manage crises effectively and minimize potential disruptions.
- Conducting internal audits prepares organizations for ISO 45001 certification by identifying areas for improvement and ensuring compliance with the standard’s requirements.
What is ISO 45001 Software?
ISO 45001 software facilitates the implementation and maintenance of an occupational health and safety management system aligned with ISO 45001 requirements.
Key Features & Benefits of ISO 45001 Software
- Customizable checklists allow you to address specific workplace hazards and regulatory requirements pertinent to your industry. Aligning digital checklists with health and safety SOPs and safe operating procedures ensures consistency in safety protocols and makes ISO 45001 assessments more effective.
- Transitioning from manual reporting to real-time, automated systems significantly boosts efficiency. ISO 45001 software enables instant generation of reports that can be customized and shared with relevant stakeholders. This not only saves considerable time and effort but also enhances decision-making processes.
- ISO 45001 software facilitates the identification and implementation of corrective actions when safety incidents or non-conformities occur. Addressing these issues reduces the likelihood of recurrence, ensuring continuous improvement in safety performance.
- Automating routine tasks and workflows minimizes the potential for human error and ensures consistent adherence to safety procedures. Processes, like incident reporting, risk assessments, and compliance tracking, can be automated, freeing up valuable resources and enhancing overall operational efficiency.
- Access to historical data allows you to monitor trends and identify recurring patterns related to workplace safety. ISO 45001 software provides valuable insights that inform proactive measures, helping to prevent future incidents and continuously improve your organization’s health and safety standards.
How to Choose the Right ISO 45001 Software?
Selecting the appropriate ISO 45001 software is crucial for effectively managing occupational health and safety within your organization. To make an informed decision, consider the following key factors:
Intuitive and User-Friendly Interface
The ISO 45001 software should offer an intuitive interface that simplifies navigation and operation. This ease of use ensures that all employees, regardless of their technical proficiency, can engage with the system effectively, leading to better compliance and participation.
Mobile Application and Offline Functionality
Having access to ISO 45001 software via mobile devices is essential. A mobile application enables employees to report incidents, access safety procedures, and perform tasks remotely. Offline functionality ensures that these capabilities remain available even without an internet connection.
For ISO 45001 specifically, check that findings carry their clause reference automatically and that nonconformity grading is built into the form rather than added afterwards in a spreadsheet.
Cost-Effectiveness
Evaluate the total cost of ownership, including initial setup, licensing fees, maintenance, and any additional expenses. The ISO 45001 software should provide a balance between cost and functionality, delivering the necessary features without unnecessary expenditure.
Reliable Customer Support
Dependable customer support is vital for resolving issues promptly and minimizing downtime. Ensure that the software provider offers comprehensive support services, including training, technical assistance, and regular updates to keep the system current with evolving standards.
Customer Reviews and Testimonials
Investigate feedback from current users to gauge the software’s performance and reliability. Customer reviews and testimonials provide insights into real-world experiences, highlighting strengths and potential limitations that may not be evident from product descriptions alone.
Free Trials and Personalized Demos
Use free trials and personalized demonstrations to assess the software’s suitability for your organization’s specific needs. These opportunities allow you to explore features firsthand, evaluate user-friendliness, and determine how well the software aligns with your OHSMS objectives.

FAQs
No. ISO 45001 is a voluntary standard. Customers, main contractors, or public tenders may require it as a condition of work, but no law requires certification in itself.
ISO 45001 does not list a set number of mandatory procedures. It requires “documented information” in specific clauses, such as the scope, the OH&S policy, hazard and risk processes, legal requirements, objectives, emergency plans, monitoring results, internal audit and management review results, and incident and corrective action records.
At least once a year during the three-year certification cycle, with a recertification audit before the certificate expires.
ISO 45001:2018, as amended by ISO 45001:2018/Amd 1:2024, which added climate change considerations. A revised edition is expected in the first half of 2027.
ISO 45001 replaced OHSAS 18001. It uses the common ISO management system structure, puts more weight on the context of the organization, leadership, and worker participation, and treats OH&S as part of business planning. OHSAS 18001 certificates stopped being valid when the migration period ended on 30 September 2021.
Any competent person who is objective and impartial, which usually means they do not audit their own work. Organizations use trained staff from other departments or an external auditor working on their behalf.
A major nonconformity means a requirement is not met in a way that undermines the system’s ability to achieve its intended results. A minor nonconformity is a gap that does not. Certification bodies usually expect majors to be corrected and verified before certification is granted.