- Library ›
- ISO Standards ›
- ISO 9001 2015 Surveillance Audit Checklist
ISO 9001 2015 Surveillance Audit Checklist
60 questions in 8 sectionsInteractive preview: try the answers
Section 1 of 8 · 8 questionsPhase 1 — Pre-Audit Preparation
The date, duration, and scope of the surveillance audit has been confirmed with the certification body, including which processes, sites, and clauses are in scope for this visit.
The previous surveillance audit report (or Stage 2 certification audit report if this is the first surveillance) has been retrieved and reviewed, with all findings and observations documented.
A register of all nonconformities raised at the previous audit is available, showing the status of each corrective action — open, in progress, or closed with verified evidence.
All major nonconformities from the previous audit have been closed with verified corrective actions before the surveillance audit date; any outstanding minor nonconformities have documented progress toward closure.
Key personnel who will be interviewed or observed during the surveillance audit have been briefed on the audit process, the scope of this visit, and their role in presenting evidence.
The QMS document register is current, with all procedures, work instructions, and forms at their correct revision level and accessible to auditors.
Records required as evidence of QMS operation — including internal audit reports, management review minutes, corrective action records, training records, and monitoring data — have been collated and are ready for auditor review.
Any significant changes to the organisation, its processes, its scope, or its documented information since the last audit have been identified and documented, ready to be presented to the auditor.
Section 2 of 8 · 8 questionsPhase 2 — Previous Audit Findings And Corrective Action Closure
A corrective action register or equivalent is maintained, documenting every nonconformity and observation raised at the previous audit, the root cause analysis performed, the corrective action implemented, and the evidence of effectiveness verification (Clause 10.2).
Root cause analysis has been performed for each nonconformity using a documented method — such as 5 Whys, fishbone analysis, or equivalent — and the root cause is clearly documented alongside the corrective action taken (Clause 10.2.1).
Corrective actions address the root cause of each nonconformity, not just the immediate symptom, and there is evidence that the systemic issue has been resolved (Clause 10.2.1).
Effectiveness of each corrective action has been verified — either through re-audit, process monitoring, or another defined method — and the verification outcome is documented before the nonconformity is marked as closed (Clause 10.2.2).
Where a corrective action required a change to documented information — such as a procedure update, a new work instruction, or a revised form — that change has been made and the updated document is at the correct revision level (Clauses 7.5 and 10.2).
Corrective actions taken in response to previous audit findings have been communicated to relevant personnel, and those personnel are aware of the changes made to processes or documentation as a result (Clauses 7.3 and 7.4).
There is no recurrence of nonconformities that were closed at the previous audit — if recurrence has occurred, a further corrective action has been raised and is being managed (Clause 10.2).
Observations and opportunities for improvement noted at the previous audit — even where no formal corrective action was required — have been considered, with a documented rationale for actions taken or not taken (Clause 10.3).
Section 3 of 8 · 8 questionsPhase 3 — Internal Audit Programme
An internal audit programme is documented and maintained, covering all QMS processes and all applicable clauses of ISO 9001:2015 across the certification cycle (Clause 9.2.1).
The internal audit programme shows that all processes within the QMS scope have been audited at least once since the last surveillance or certification audit (Clause 9.2.1).
Internal audits have been conducted at planned intervals and evidence of their completion — including audit plans, audit reports, and attendance records — is available for auditor review (Clause 9.2.2).
Internal auditors are independent of the processes they audit and have the competence to audit against ISO 9001:2015 requirements, with evidence of auditor training or qualification available (Clause 9.2.1).
Internal audit reports document the scope, criteria, findings, conformities, nonconformities, and any observations from each audit, and are retained as documented information (Clause 9.2.2).
Nonconformities identified during internal audits have been raised as corrective actions, with root cause analysis performed and corrective actions implemented and verified (Clauses 9.2.2 and 10.2).
The internal audit programme has been adjusted where necessary to reflect changes in process risk, organisational changes, or findings from previous audits (Clause 9.2.1).
Internal audit results have been reported to relevant management and used as an input to the management review (Clauses 9.2.2 and 9.3.2).
Section 4 of 8 · 7 questionsPhase 4 — Management Review
At least one management review has been conducted since the last surveillance or certification audit, with documented evidence of top management participation (Clause 9.3.1).
Management review meeting minutes or equivalent documented information are retained, covering the date, attendees, agenda items discussed, decisions made, and actions assigned (Clause 9.3).
Management review inputs covered all required topics specified in Clause 9.3.2, including: status of actions from previous reviews; changes in external and internal issues; QMS performance data including quality objectives, customer satisfaction, process performance, nonconformity and corrective action trends, monitoring and measurement results, audit findings, and supplier performance; adequacy of resources; and opportunities for improvement (Clause 9.3.2).
Management review outputs include documented decisions on improvement opportunities, any need for changes to the QMS, and resource requirements, with assigned owners and target dates for each action (Clause 9.3.3).
Actions arising from the management review have been assigned to responsible owners, tracked to completion, and their status is documented and available for review (Clause 9.3.3).
Actions from the previous management review have been followed up, with completed actions evidenced and any outstanding actions with documented progress and revised target dates (Clause 9.3.3).
The management review demonstrated genuine top management engagement with QMS performance — not just attendance — including evidence that decisions were made and resources allocated based on the review findings (Clause 5.1.1).
Section 5 of 8 · 8 questionsPhase 5 — Quality Objectives And Performance Data
Quality objectives are documented, measurable, and have been monitored throughout the period since the last audit, with performance data available for auditor review (Clause 6.2).
Quality objectives performance data is current and shows the trend in performance over the period, not just a snapshot at the time of audit (Clause 9.1.1).
Where quality objectives have not been achieved, there is a documented explanation of the shortfall and evidence of corrective or improvement action taken or planned in response (Clauses 6.2 and 10.3).
Quality objectives have been reviewed for continued relevance and updated where organisational priorities, customer requirements, or performance trends have changed since the last audit (Clause 6.2).
Quality objectives have been communicated to relevant personnel and there is evidence that those personnel are aware of the objectives relevant to their role (Clauses 6.2 and 7.3).
Process performance data — including product or service conformity rates, delivery performance, customer complaint volumes, and nonconformance rates — is collected, analysed, and used to evaluate QMS effectiveness (Clause 9.1.1).
Monitoring and measurement activities are carried out using calibrated or verified equipment where measurement accuracy is critical, with calibration records available (Clause 7.1.5).
Performance data has been analysed to identify trends, evaluate the need for improvement, and assess the effectiveness of actions previously taken (Clause 9.1.3).
Section 6 of 8 · 7 questionsPhase 6 — Customer Focus And Complaints
Customer satisfaction is monitored through defined methods — such as surveys, delivery performance data, complaint analysis, or customer feedback reviews — and results are documented and analysed (Clause 9.1.2).
Customer satisfaction data has been reviewed at management review and used to identify improvement opportunities or corrective actions where satisfaction levels are below expectations (Clauses 9.1.2 and 9.3.2).
A customer complaint register or equivalent is maintained, recording all complaints received since the last audit, the date received, the nature of the complaint, the action taken, and the outcome (Clauses 8.5.5 and 10.2).
Customer complaints have been investigated, with root cause analysis performed for significant or recurring complaints and corrective actions implemented and verified (Clause 10.2).
Customer complaint trends have been analysed to identify systemic issues, and improvement actions have been taken where patterns indicate a recurring quality or service delivery problem (Clauses 9.1.3 and 10.3).
Customer requirements have been reviewed and are being met — delivery performance, product conformity, and any contractual quality requirements are monitored and evidence is available (Clauses 8.2.3 and 9.1.2).
Where post-delivery obligations exist — such as warranty, service, or maintenance requirements — these are being managed and records are available (Clause 8.5.5).
Section 7 of 8 · 7 questionsPhase 7 — Changes Since The Last Audit
A record of significant changes to the organisation since the last audit is available, including changes to: organisational structure or key personnel; products or services offered; processes or production methods; sites or locations within scope; suppliers or outsourced activities; applicable regulatory or customer requirements; and the QMS scope or documented information (Clause 6.3).
Changes to QMS processes have been planned and controlled through a documented change management process, with risk assessment performed before significant changes were implemented (Clause 6.3).
Changes to documented information — including new or revised procedures, work instructions, forms, or records — are at the correct revision level, have been approved, and have been communicated to relevant personnel (Clause 7.5.3).
Where key personnel in QMS roles have changed since the last audit — including the management representative, process owners, or internal auditors — their competence has been verified and documented, and relevant handover or training has been completed (Clause 7.2).
Where new products, services, or processes have been introduced since the last audit, the appropriate QMS controls — including risk assessment, operational planning, traceability, and nonconformance management — have been extended to cover them (Clauses 6.1 and 8.1).
Where outsourced activities or suppliers have changed since the last audit, the supplier evaluation and control process has been applied to new external providers, and relevant controls are in place (Clause 8.4).
The certification body has been notified of any changes that could affect the scope, boundaries, or applicability of the ISO 9001 certificate, in accordance with the certification agreement.
Section 8 of 8 · 7 questionsPhase 8 — Continual Improvement Evidence
Evidence of continual improvement activities since the last audit is documented and available, demonstrating that the QMS is actively developing rather than being maintained as a static system (Clause 10.3).
Improvement activities go beyond corrective actions for nonconformities and include proactive improvements to process efficiency, product or service quality, customer satisfaction, or QMS effectiveness (Clause 10.3).
Improvement actions are tracked through a defined process, with assigned owners, target dates, and documented outcomes confirming the improvement achieved (Clause 10.3).
The results of improvement activities are measured where possible, with before-and-after data or other objective evidence demonstrating the benefit of the improvement (Clause 9.1.3).
Continual improvement opportunities identified through internal audits, management reviews, customer feedback, process performance analysis, and corrective action trends have been evaluated and, where appropriate, acted upon (Clauses 9.1.3, 9.2, 9.3, and 10.3).
There is evidence that the QMS has improved in effectiveness since the last audit — for example, through improved quality objectives performance, reduced complaint volumes, improved process performance data, or reduced nonconformance rates (Clause 10.3).
The organisation can demonstrate that the Plan-Do-Check-Act cycle is operating in practice — processes are planned, implemented, monitored against criteria, and adjusted based on results (Clause 10.3).
Checklist by GoAudits. This checklist is an example: we do not guarantee compliance with the laws applicable to your territory or industry. Seek professional advice to adapt it to your workplace or jurisdiction.
Free PDF
Download the ISO 9001 2015 Surveillance Audit Checklist
By downloading this checklist you agree to the GoAudits privacy policy and terms of service.
NEW! Try generating a custom checklist with our free AI tool:
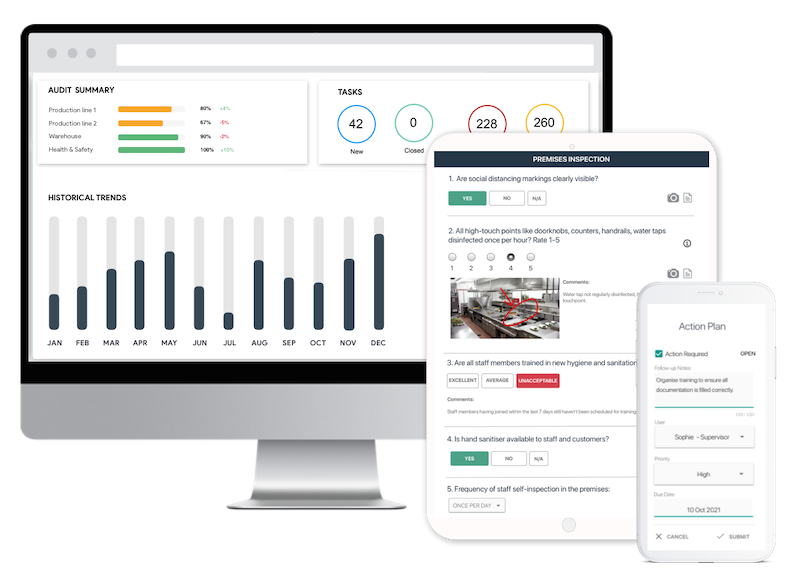
Easy inspection app for your digital checklists
- Conduct inspections anytime, anywhere - even offline
- Capture photos as proof of compliance or areas needing attention
- Instantly generate and share detailed reports after the inspections
- Assign & track follow-up tasks, view historical trends on a centralized dashboard