- Library ›
- ISO Standards ›
- ISO 42001 Checklist
ISO 42001 Checklist
157 questions in 45 sectionsInteractive preview: try the answers
Section 1 of 45 · 10 questionsClause 4 — Context Of The Organization
The organization has documented the external issues relevant to its AIMS, including applicable AI regulations, industry standards, and market expectations.
Internal issues affecting the AIMS are documented, including organizational culture, existing governance structures, and resource capabilities.
Interested parties relevant to the AIMS are identified, including customers, users, regulators, employees, and third-party AI vendors.
The requirements and expectations of each interested party are documented and reviewed periodically.
The AIMS scope statement is documented, clearly defining which AI systems, activities, and organizational units are covered.
AI systems included within scope are identified by name, function, and the organization's role (developer, provider, or deployer).
Any AI systems excluded from scope are listed with documented justification.
The AIMS scope is available to relevant interested parties.
An AI system inventory is maintained and aligned to the documented scope.
The AI system inventory includes system purpose, owner, operational status, and data inputs for each entry.
Section 2 of 45 · 11 questionsClause 5 — Leadership And AI Policy
Top management has demonstrated commitment to the AIMS through documented resource allocation decisions and governance approvals.
Evidence of leadership involvement in AIMS establishment is available, such as steering committee records, approval sign-offs, or management review minutes.
An AI policy is documented and approved by top management.
The AI policy includes a commitment to responsible and ethical AI development and use.
The AI policy provides a framework for setting AI objectives and includes a commitment to continual improvement.
The AI policy is communicated to all personnel involved in AI activities.
The AI policy is available to relevant external parties where appropriate.
AIMS roles, responsibilities, and authorities are documented and assigned.
Responsibility for ensuring AIMS conformity is formally assigned to a named role or individual.
Responsibility for reporting AIMS performance to top management is formally assigned.
Evidence that AIMS responsibilities have been communicated to relevant personnel is available.
Section 3 of 45 · 14 questionsClause 6 — AI Risk Assessment And Planning
An AI risk assessment process is documented, including risk identification, analysis, evaluation, and treatment steps.
Risk criteria are defined, including AI-specific criteria such as bias potential, explainability requirements, and societal impact thresholds.
Risk assessments have been completed for all AI systems within scope.
Risk assessments are reviewed and updated when AI systems undergo significant changes.
A risk register is maintained with risk owners, risk levels, and treatment status for each identified risk.
Risk treatment options have been selected for each identified risk, with documented rationale.
A Statement of Applicability (SoA) is documented, listing applicable Annex A controls with justifications for inclusions and exclusions.
A risk treatment plan is documented with assigned owners and target completion dates.
An AI impact assessment process is documented, covering intended use cases and foreseeable misuse scenarios.
Impact assessments have been completed for AI systems with potential to affect individuals or society.
Impact assessment results are retained and reviewed when system purpose or deployment context changes.
AI objectives are established, documented, measurable, and consistent with the AI policy.
Plans to achieve AI objectives include assigned responsibilities, required resources, timelines, and evaluation methods.
A change management process is documented for planned changes to the AIMS, including changes to AI systems, data sources, or use cases.
Section 4 of 45 · 12 questionsClause 7 — Support: Resources, Competence, And Documentation
Resources required to establish, implement, and maintain the AIMS are determined and provided.
Budget allocation for AIMS activities is visible and documented.
Competence requirements are defined for all roles that affect AI system performance, safety, or governance.
Evidence of competence is available for personnel in AIMS roles, such as qualifications, training records, or assessed performance.
Training records are maintained where competence was developed through formal training.
Evidence that training effectiveness has been evaluated is available.
Personnel involved in AI activities are aware of the AI policy and their contribution to AIMS objectives.
Internal and external communication requirements for the AIMS are documented, specifying who communicates what, to whom, and by which channel.
A document control procedure is in place covering creation, approval, version control, and access management.
AIMS documents are properly identified, described, and protected from unauthorized changes.
Retention and disposal requirements for AIMS documented information are defined.
Documented information is accessible to those who need it and protected from unintended alteration or deletion.
Section 5 of 45 · 14 questionsClause 8 — Operation
Operational procedures are documented for AI system design, development, testing, deployment, monitoring, and decommissioning.
Criteria for controlling AI lifecycle processes are established and applied consistently.
Evidence that AI lifecycle processes are executed according to documented procedures is available.
AI risk assessments are performed at the design stage before new AI systems are deployed.
AI risk assessments are repeated following significant changes to model architecture, training data, use case, or deployment environment.
Change control records document approvals for model updates, prompt changes, retraining runs, and vendor changes.
Rollback procedures are defined and tested for AI systems where reverting to a prior version may be required.
Human oversight mechanisms are defined for AI systems where automated decisions carry material risk to individuals or the organization.
Human review and override records are maintained for AI systems with defined oversight requirements.
Model performance is tested against defined criteria before deployment, including accuracy, robustness, and intended-use alignment.
Post-deployment monitoring is in place to detect model drift, performance degradation, and unexpected outputs.
Monitoring results and incidents are recorded and reviewed at defined intervals.
AI-specific incident response procedures are documented and cover detection, containment, root cause analysis, and notification.
Records of AI incidents and near-misses are maintained and used to inform corrective action.
Section 6 of 45 · 12 questionsClause 9 — Performance Evaluation And Internal Audit
The organization has determined what to monitor and measure for AIMS performance, including AI system outcomes, risk treatment effectiveness, and objective progress.
Methods, frequency, and responsibility for monitoring and measurement are documented.
Monitoring results are analyzed, evaluated, and reported to relevant management at defined intervals.
An internal audit program is documented, covering audit scope, criteria, frequency, and auditor selection.
Auditor independence from the areas being audited is ensured and documented.
At least one complete internal AIMS audit cycle has been completed before the certification audit.
Internal audit reports document findings, evidence reviewed, conformities, and nonconformities.
Audit findings are communicated to relevant management and tracked to closure.
Management reviews are conducted at planned intervals by top management.
Management review inputs include AIMS performance data, audit results, risk register status, objective progress, and changes in internal or external context.
Management review outputs include decisions on improvement opportunities, resource needs, and any required changes to the AIMS.
Management review minutes are retained as documented evidence.
Section 7 of 45 · 10 questionsClause 10 — Improvement And Corrective Action
A process for identifying, recording, and managing nonconformities is documented.
Nonconformities, including AI system control failures and incidents, are recorded when they occur.
Root cause analysis is performed for each nonconformity to identify the underlying cause rather than the symptom.
Corrective actions are planned with assigned owners and target completion dates.
Corrective actions are verified for effectiveness before the nonconformity is closed.
Records of nonconformities, corrective actions, and closure evidence are retained.
Lessons learned from nonconformities and AI incidents are used to update risk assessments, controls, and procedures.
Improvement opportunities are identified through monitoring results, audit findings, management reviews, and incident analysis.
Evidence of continual improvement activities is available, demonstrating that the AIMS is developed over time rather than maintained as a static system.
Improvement actions are tracked and their outcomes reported at management reviews.
Section 8 of 45 · 4 questionsA.2.2 — AI Policy
A written AI policy is documented and approved at the appropriate management level, setting out the organisation's approach to developing, providing, and using AI systems.
The AI policy is informed by the organisation's business strategy, values, risk appetite, legal obligations, and the risk environment relevant to its AI activities.
The AI policy includes principles that guide all AI-related activities and processes for handling exceptions to those principles.
Evidence is available that the AI policy genuinely shapes decision-making about AI systems, rather than existing solely as a document.
Section 9 of 45 · 3 questionsA.2.3 — Alignment With Other Organisational Policies
The organisation has identified all existing policies — including information security, privacy, risk management, HR, procurement, and ethics — that intersect with AI activities.
The AI policy is consistent with those existing policies, with conflicts identified and resolved through policy updates rather than left unaddressed.
Where AI activities introduce requirements not covered by existing policies, the AI policy or relevant existing policies have been updated to address them.
Section 10 of 45 · 3 questionsA.2.4 — Review Of The AI Policy
A named, management-approved role is responsible for the periodic review of the AI policy.
The AI policy is reviewed on a planned cycle and whenever material changes occur, including new regulations, new AI use cases, changes in organisational context, or lessons learned from incidents.
Review outcomes — including any resulting policy changes — are documented and retained as records.
Section 11 of 45 · 3 questionsA.3.2 — AI Roles And Responsibilities
AI-specific roles and responsibilities are defined and documented, covering the full AI system life cycle — including risk management, impact assessment, development, oversight, data quality, security, and supplier management.
Accountability and responsibility for each AI-related activity are explicitly assigned to named roles, with no gaps in coverage.
AI roles and responsibilities are communicated to relevant personnel and reflected in organisational structures.
Section 12 of 45 · 3 questionsA.3.3 — Reporting Of Concerns Regarding AI Systems
A formal mechanism exists for personnel, contractors, and relevant external parties to raise concerns about the organisation's development, provision, or use of AI systems.
The reporting mechanism is accessible, confidential where appropriate, and protected from retaliation.
Defined investigation and escalation steps are documented for concerns raised through this mechanism, and records of concerns raised and their resolution are retained.
Section 13 of 45 · 2 questionsA.4.2 — Resource Documentation
An inventory of resources required by each AI system across its life cycle is maintained, covering data, tooling, system and computing resources, and human expertise.
Checklist by GoAudits. This checklist is an example: we do not guarantee compliance with the laws applicable to your territory or industry. Seek professional advice to adapt it to your workplace or jurisdiction.
Free PDF
Download the ISO 42001 Checklist
By downloading this checklist you agree to the GoAudits privacy policy and terms of service.
NEW! Try generating a custom checklist with our free AI tool:
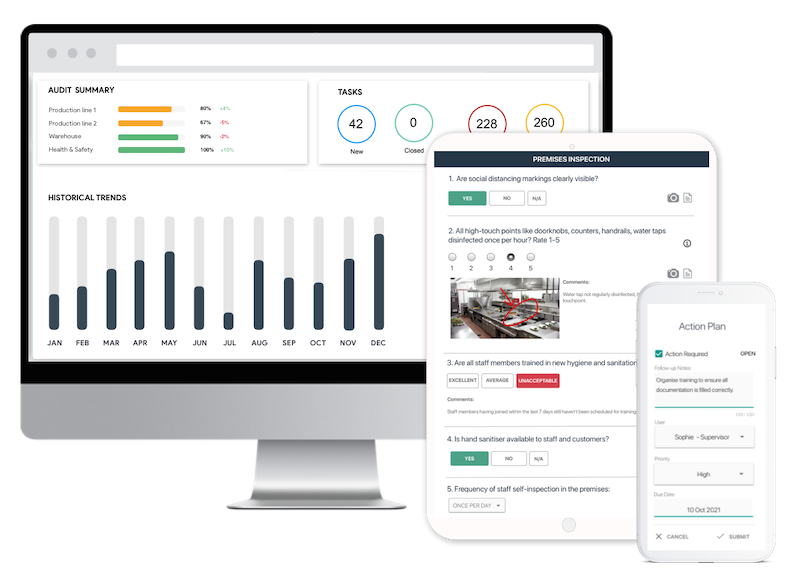
Easy inspection app for your digital checklists
- Conduct inspections anytime, anywhere - even offline
- Capture photos as proof of compliance or areas needing attention
- Instantly generate and share detailed reports after the inspections
- Assign & track follow-up tasks, view historical trends on a centralized dashboard