- Library ›
- ISO Standards ›
- ISO 28000 Checklist
ISO 28000 Checklist
83 questions in 7 sectionsInteractive preview: try the answers
Section 1 of 7 · 10 questionsClause 4 — Context Of The Organization
Internal and external issues relevant to the organization's purpose and that affect its ability to achieve the intended outcomes of its security management system (SMS) are identified and documented.
Internal issues are reviewed and include organizational structure, existing security practices, workforce capability, technology infrastructure, and the nature and complexity of operations and supply chain activities.
External issues are reviewed and include the threat environment, regulatory and statutory security requirements, geopolitical factors, sector-specific security risks, and the security practices of supply chain partners.
The security environment in which the organization operates is assessed, including dependencies and interdependencies within and beyond the supply chain.
Interested parties relevant to the SMS are identified, including customers, regulators, law enforcement agencies, supply chain partners, insurers, and personnel.
The requirements and expectations of each interested party are documented, including any contractual, regulatory, or voluntary security obligations the organization subscribes to.
The scope of the SMS is documented, defining which operations, sites, supply chain activities, assets, and organizational units are included.
Any operations or activities excluded from the SMS scope are listed with documented justification.
The scope is made available to relevant interested parties.
The processes needed to establish, implement, maintain, and continually improve the SMS are identified and documented.
Section 2 of 7 · 9 questionsClause 5 — Leadership
Top management has demonstrated commitment to the SMS through visible endorsement, resource allocation, and active participation in security governance.
A security management policy is documented and approved by top management.
The security policy includes commitments to protecting people, assets, information, infrastructure, and supply chain operations against security threats and incidents.
The security policy includes a commitment to meeting applicable statutory, regulatory, and voluntary security obligations and to continually improving the SMS.
The security policy provides a framework for setting and reviewing security objectives.
The security policy is communicated to all personnel with roles relevant to security management.
The security policy is made available to relevant external interested parties, including key supply chain partners and regulators, where appropriate.
SMS roles, responsibilities, and authorities are documented and assigned, including accountability for SMS conformity, security risk management, and incident response.
Evidence that SMS roles and responsibilities have been communicated to relevant personnel is available.
Section 3 of 7 · 12 questionsClause 6 — Planning
The organization has a documented process for identifying security-related risks and opportunities that could affect the SMS and its intended outcomes.
Security risk assessments are conducted using a systematic methodology that covers threat identification, vulnerability analysis, and assessment of the potential consequences of security incidents.
Security risk assessments address risks to people, physical assets, information, data, infrastructure, equipment, transportation, and supply chain operations.
Security risk assessments consider both internal threats (insider risk, access abuse) and external threats (theft, sabotage, terrorism, cargo tampering, cybersecurity threats affecting operational security).
Risk assessments are reviewed and updated at defined intervals and following significant changes to operations, the threat environment, or supply chain arrangements.
A security risk register is maintained with risk owners, assessed risk levels, and treatment status for each identified risk.
Risk treatment options have been selected for each identified security risk, with documented rationale for the controls chosen.
A Statement of Applicability or equivalent document records which security controls are applicable, with justification for inclusions and exclusions.
Security objectives are established, documented, and measurable.
Security objectives are consistent with the security policy and address the priority risks identified in the risk assessment.
Plans to achieve security objectives include assigned responsibilities, required resources, timelines, and methods for evaluating results.
A change management process is in place for planned changes to the SMS, operations, or supply chain arrangements that could affect the security risk profile.
Section 4 of 7 · 11 questionsClause 7 — Support
Resources required to establish, implement, maintain, and continually improve the SMS are identified and provided, including financial, human, physical, and technology resources.
Competence requirements are defined for all personnel with roles that affect security management, including security officers, site supervisors, gatekeepers, and personnel responsible for information or cargo security.
Evidence of competence is available for personnel in SMS roles, including training records, qualifications, and security-specific certifications where required.
Security awareness training is provided to all personnel who could affect the SMS, covering the security policy, individual responsibilities, threat recognition, and incident reporting procedures.
Training records are maintained and evidence that training effectiveness has been evaluated is available.
Personnel are aware of the security policy, the risks relevant to their role, and the consequences of failing to comply with security requirements.
Personnel involved in security-sensitive roles are subject to appropriate background checks or vetting consistent with the organization's security risk assessment and applicable regulatory requirements.
Internal and external communication requirements for the SMS are documented, including communication protocols for sharing threat information with supply chain partners, regulators, and law enforcement.
A document control procedure is in place covering the creation, approval, version control, access management, and retention of SMS documented information, including risk assessments, security plans, and incident records.
Documented information classified as sensitive is protected against unauthorized access, modification, or disclosure.
Retention requirements for SMS documented information are defined and applied.
Section 5 of 7 · 17 questionsClause 8 — Operation
Operational planning and control procedures are documented for all security-relevant activities within the SMS scope.
Criteria for controlling security management processes are established and consistently applied.
Evidence that security controls are implemented and maintained according to documented procedures is available.
A security threat and vulnerability assessment process is applied at defined intervals and before significant operational changes, covering all assets and activities within scope.
Physical security controls are in place to protect people, facilities, equipment, vehicles, and cargo against unauthorized access, theft, sabotage, and damage.
Access control procedures are documented and enforced for all facilities and restricted areas within the SMS scope, including visitor management, contractor access, and vehicle access controls.
Physical security measures — including fencing, lighting, locks, barriers, CCTV, and alarm systems — are maintained, tested at defined intervals, and records of testing and maintenance are retained.
Personnel security controls are implemented, including identity verification for site access, key and access card management, and procedures for managing access rights when personnel leave or change roles.
Cargo and goods security procedures are documented and applied throughout the supply chain, including sealing, tamper detection, chain of custody controls, and verification of cargo integrity at handover points.
Procedures are in place to verify the identity and authorization of supply chain partners, carriers, and service providers before entrusting them with goods, information, or access to facilities.
A process is in place to assess the security practices of supply chain partners whose operations could affect the organization's security risk profile, with documented outcomes and follow-up actions.
Information and data security controls are applied to protect security-sensitive information, including access restrictions, classification, secure transmission, and disposal of security records.
Procedures are in place for detecting, reporting, and responding to security incidents, including physical security breaches, cargo tampering, theft, unauthorized access, and threats to personnel safety.
A security incident response plan is documented, tested at defined intervals, and covers escalation, containment, notification of relevant authorities, business continuity, and recovery.
Security incident records are maintained, including the nature of the incident, response actions taken, root cause analysis, and corrective measures implemented.
Emergency response and crisis management procedures are in place for high-impact security events, with defined roles, communication protocols, and coordination arrangements with law enforcement and regulators.
Security controls applied to information technology and operational technology systems that support supply chain security are identified and maintained, including controls over remote access, network security, and system integrity.
Section 6 of 7 · 15 questionsClause 9 — Performance Evaluation
The organization has determined what to monitor and measure for SMS performance, including security incident frequency and severity, control effectiveness, threat intelligence updates, and progress against security objectives.
Methods, frequency, responsibility, and criteria for evaluating SMS monitoring and measurement results are documented.
Security performance data is collected, analyzed, and reported to relevant management at defined intervals.
Security key performance indicators are tracked over time and used to assess whether security objectives are being achieved and whether the risk treatment measures remain effective.
The threat and vulnerability environment is monitored on an ongoing basis, with processes in place to incorporate new threat intelligence into the risk assessment and control framework.
An internal audit programme for the SMS is documented, covering audit scope, criteria, frequency, and auditor selection.
The audit programme covers both management system elements (Clauses 4–10) and operational security controls (Clause 8), including physical security, supply chain security, and incident management.
Auditor independence from the security operations and processes being audited is ensured and documented.
At least one complete internal SMS audit cycle has been completed before the certification audit.
Internal audit reports document findings, evidence reviewed, conformities, and nonconformities.
Audit findings are communicated to relevant management and tracked to closure.
Management reviews of the SMS are conducted at planned intervals by top management.
Management review inputs include SMS performance data, audit results, security incident trends, risk register status, progress against security objectives, status of corrective actions, changes in the threat environment, and changes in regulatory or contractual security obligations.
Management review outputs include decisions on improvement opportunities, resource needs, and any required changes to the SMS, security policy, or security controls.
Management review minutes are retained as documented evidence.
Section 7 of 7 · 9 questionsClause 10 — Improvement
A process for identifying, recording, and managing nonconformities is documented.
Nonconformities, including security control failures, unauthorized access events, cargo security breaches, and SMS process failures, are recorded when they occur.
Root cause analysis is performed for each nonconformity to identify the underlying cause, including any systemic weaknesses in the security management framework.
Corrective actions are planned with assigned owners and target completion dates.
Corrective actions are verified for effectiveness before the nonconformity is closed.
Records of nonconformities, corrective actions, and closure evidence are retained.
Lessons learned from security incidents, near-misses, and audit findings are used to update risk assessments, security controls, incident response procedures, and SMS processes.
Improvement opportunities are identified through monitoring results, audit findings, management reviews, incident analysis, threat intelligence, and changes in the security environment or operational context.
Evidence of continual improvement of the SMS is available, demonstrating that security controls, risk management practices, and supply chain security outcomes improve over time.
Checklist by GoAudits. This checklist is an example: we do not guarantee compliance with the laws applicable to your territory or industry. Seek professional advice to adapt it to your workplace or jurisdiction.
Free PDF
Download the ISO 28000 Checklist
By downloading this checklist you agree to the GoAudits privacy policy and terms of service.
NEW! Try generating a custom checklist with our free AI tool:
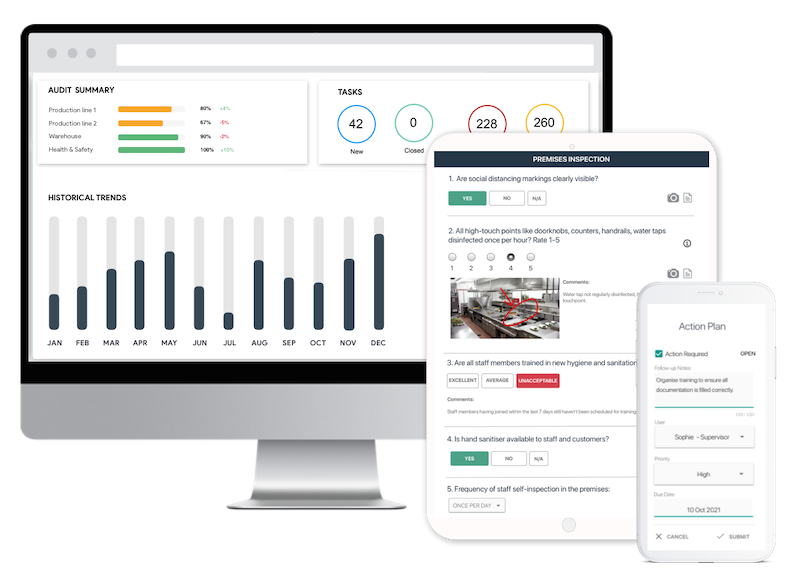
Easy inspection app for your digital checklists
- Conduct inspections anytime, anywhere - even offline
- Capture photos as proof of compliance or areas needing attention
- Instantly generate and share detailed reports after the inspections
- Assign & track follow-up tasks, view historical trends on a centralized dashboard