- Library ›
- ISO Standards ›
- ISO 27018 Checklist
ISO 27018 Checklist
54 questions in 8 sectionsInteractive preview: try the answers
Section 1 of 8 · 6 questionsConsent And Purpose Limitation
PII is processed only for the purposes explicitly agreed with the PII controller (cloud service customer), and those purposes are documented in the cloud service agreement.
PII is not used for marketing or advertising purposes without the explicit and documented consent of the PII controller or, where applicable, the individual data subject.
PII collected or processed during the delivery of cloud services is not used for purposes beyond those stated in the agreement, including profiling, analytics, or product improvement, unless separately agreed in writing.
Where consent from data subjects is required for a specific processing activity, a consent management process is in place that records consent, tracks changes to consent status, and supports consent withdrawal.
Consent records are maintained in a form that allows the organization to demonstrate that consent was obtained for each processing purpose, including the date, mechanism, and scope of consent.
Processing purpose limitations are reviewed when the scope of cloud services changes, and any expansion of processing purposes is subject to formal re-agreement with the PII controller.
Section 2 of 8 · 6 questionsPII Inventory And Data Minimization
A PII inventory is maintained, documenting the categories of PII processed on behalf of each cloud service customer, the processing activities performed, and the locations (cloud regions or data centers) where PII is stored or processed.
Data minimization controls are applied to ensure that only PII necessary for the agreed processing purposes is collected, retained, or accessible within cloud environments.
PII is classified according to sensitivity, and classification labels inform access controls, encryption requirements, and retention schedules applied to cloud-hosted PII.
Data flows involving PII — including transfers between cloud services, regions, or third-party sub-processors — are documented and kept current.
Temporary files, caches, and working copies of PII generated during cloud processing are identified and subject to secure erasure procedures once the processing activity is complete.
PII minimization requirements are communicated to development and operations teams responsible for designing and maintaining cloud services that process PII.
Section 3 of 8 · 7 questionsAccess Control And Identity Management
Access to PII stored or processed in cloud environments is restricted to authorized personnel with a documented business need, enforced through role-based access controls or equivalent.
Privileged access to cloud infrastructure, databases, and storage systems containing PII is subject to enhanced controls including multi-factor authentication, just-in-time access provisioning, and session logging.
A formal process exists for provisioning, reviewing, and revoking access to PII in cloud environments, with access rights reviewed at defined intervals and immediately upon role change or departure.
Cloud administrator access to PII is logged, with logs retained for a defined period and protected against unauthorized access or deletion.
Access logs for PII stored in cloud environments are reviewed at defined intervals for anomalous or unauthorized access patterns.
Where cloud service customers require the ability to manage their own access controls for PII they store in the cloud service, tools or interfaces are provided to enable this, and their use is documented.
Authentication mechanisms for access to cloud-hosted PII meet the security requirements of the most sensitive PII category held within the environment.
Section 4 of 8 · 7 questionsTransparency And Disclosure To PII Controllers
Cloud service agreements include clear and specific terms covering how PII will be processed, stored, protected, and deleted, without requiring PII controllers to accept vague or broadly worded data processing provisions.
The organization discloses the names and locations of all sub-processors that may access or process PII on behalf of cloud service customers before the contract is signed.
Where the organization intends to change sub-processors during the contract period, PII controllers are notified in advance and provided with the right to object to the change or terminate the agreement without penalty.
A register of sub-processors is maintained, including their name, location, the processing activities they perform, and the data protection obligations imposed on them by contract.
The organization makes available to PII controllers all information necessary to verify compliance with PII protection obligations, including the results of third-party audits, certifications, or compliance assessments where direct customer audits of multi-tenant cloud infrastructure are impractical.
Information about data processing locations — including cloud regions, availability zones, and any cross-border transfer mechanisms — is disclosed to PII controllers in the service agreement or associated documentation.
Changes to the geographic locations where PII is stored or processed are disclosed to PII controllers and are subject to any contractual restrictions on data residency.
Section 5 of 8 · 5 questionsSub-Processor Management
All sub-processors with access to PII processed on behalf of cloud service customers are bound by written data processing agreements imposing PII protection obligations equivalent to those in the organization's customer agreements.
Sub-processors are assessed before engagement to confirm they have appropriate technical and organizational measures in place to protect PII, including relevant certifications or audit results.
Sub-processor access to PII is limited to what is necessary for the sub-processor's specific function and is controlled through technical access restrictions.
Sub-processors are monitored for compliance with their contractual PII protection obligations, and any issues identified are addressed and documented.
On termination of a sub-processor relationship, PII held by the sub-processor is returned or securely deleted, with confirmation provided to the organization.
Section 6 of 8 · 7 questionsPII Retention And Secure Deletion
Retention schedules are defined for all categories of PII processed in cloud environments, specifying the maximum period for which PII is retained and the trigger for deletion.
Retention schedules are documented in or referenced by the cloud service agreement, enabling PII controllers to understand and agree to retention practices.
Automated deletion or anonymization processes are in place to enforce retention schedules where technically feasible, with manual deletion procedures documented for environments where automation is not available.
Secure deletion procedures are applied when PII is deleted from cloud storage, ensuring data cannot be recovered from deleted files, database records, or storage media.
On termination of the cloud service agreement, all PII belonging to the customer is deleted or returned in a documented format within the timeframe specified in the agreement, with written confirmation of deletion provided to the PII controller.
Backup copies of PII are subject to the same retention and deletion requirements as primary copies, and deletion from backups is tracked and confirmed.
Physical media containing PII that is decommissioned from cloud environments is securely destroyed using documented procedures, with destruction certificates retained.
Section 7 of 8 · 6 questionsPII Breach Detection And Notification
Processes are in place to detect, investigate, and classify security incidents involving PII stored or processed in cloud environments, including unauthorized access, accidental disclosure, and ransomware or malicious destruction.
PII breaches are reported to affected PII controllers without undue delay following confirmation of the incident, within the timeframe specified in the cloud service agreement or applicable regulatory requirements.
Breach notifications to PII controllers include sufficient detail to enable them to meet their own notification obligations, including the nature of the incident, categories and approximate volume of PII affected, likely consequences, and containment measures taken.
Breach notification records are maintained, documenting when the breach was detected, when the PII controller was notified, and the content of notifications sent.
Post-incident reviews are conducted following PII breaches, with root cause analysis, corrective actions, and lessons learned documented and used to improve controls.
PII-specific breach scenarios are included in the organization's incident response plan and tested at defined intervals through tabletop exercises or simulations.
Section 8 of 8 · 10 questionsAnnex A — Extended PII Controls For Public Cloud Processors
The organization does not use PII processed on behalf of cloud service customers to develop, train, or improve its own products or services without explicit documented consent from the PII controller.
Where PII is transferred to a third country or international organization, the legal basis for the transfer is documented, verified, and disclosed to the PII controller.
The organization responds to requests from PII controllers to access, correct, restrict, or delete individual data subjects' PII held in the cloud environment, within the timeframes and through the mechanisms specified in the service agreement.
Interfaces or mechanisms are provided to enable PII controllers to retrieve their PII in a structured, commonly used format to support data portability obligations where applicable.
The organization does not retain PII beyond the agreed retention period, including in backups, disaster recovery systems, or analytics environments, unless retention is required by applicable law and the PII controller is notified.
Disclosure of PII to third parties — including law enforcement, regulatory bodies, or other government authorities — is subject to a documented procedure that notifies the PII controller before disclosure unless legally prohibited.
Where law enforcement or regulatory requests for PII cannot be disclosed to the PII controller due to a legal prohibition, this restriction is documented and the PII controller is informed that a disclosure has been made subject to a legal prohibition, to the extent permitted.
The organization publishes or makes available a transparency report or equivalent disclosure covering the volume and categories of government requests for PII received, to the extent permitted by applicable law.
PII processed in cloud environments is encrypted at rest and in transit, with encryption key management documented and aligned with the sensitivity of the PII held.
Personnel with access to PII in cloud environments receive role-specific privacy awareness training covering PII handling obligations, breach reporting procedures, and the consequences of unauthorized access or disclosure.
Checklist by GoAudits. This checklist is an example: we do not guarantee compliance with the laws applicable to your territory or industry. Seek professional advice to adapt it to your workplace or jurisdiction.
Free PDF
Download the ISO 27018 Checklist
By downloading this checklist you agree to the GoAudits privacy policy and terms of service.
NEW! Try generating a custom checklist with our free AI tool:
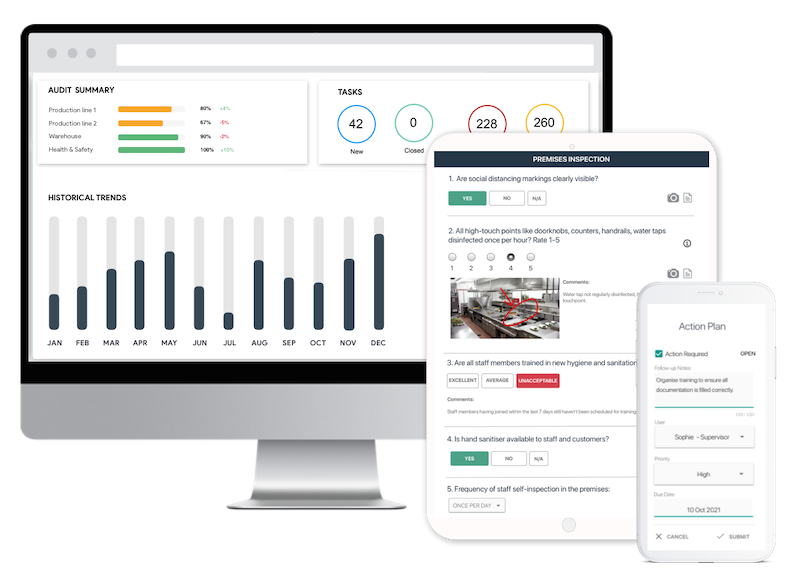
Easy inspection app for your digital checklists
- Conduct inspections anytime, anywhere - even offline
- Capture photos as proof of compliance or areas needing attention
- Instantly generate and share detailed reports after the inspections
- Assign & track follow-up tasks, view historical trends on a centralized dashboard